Table of Contents (1 sections)▾
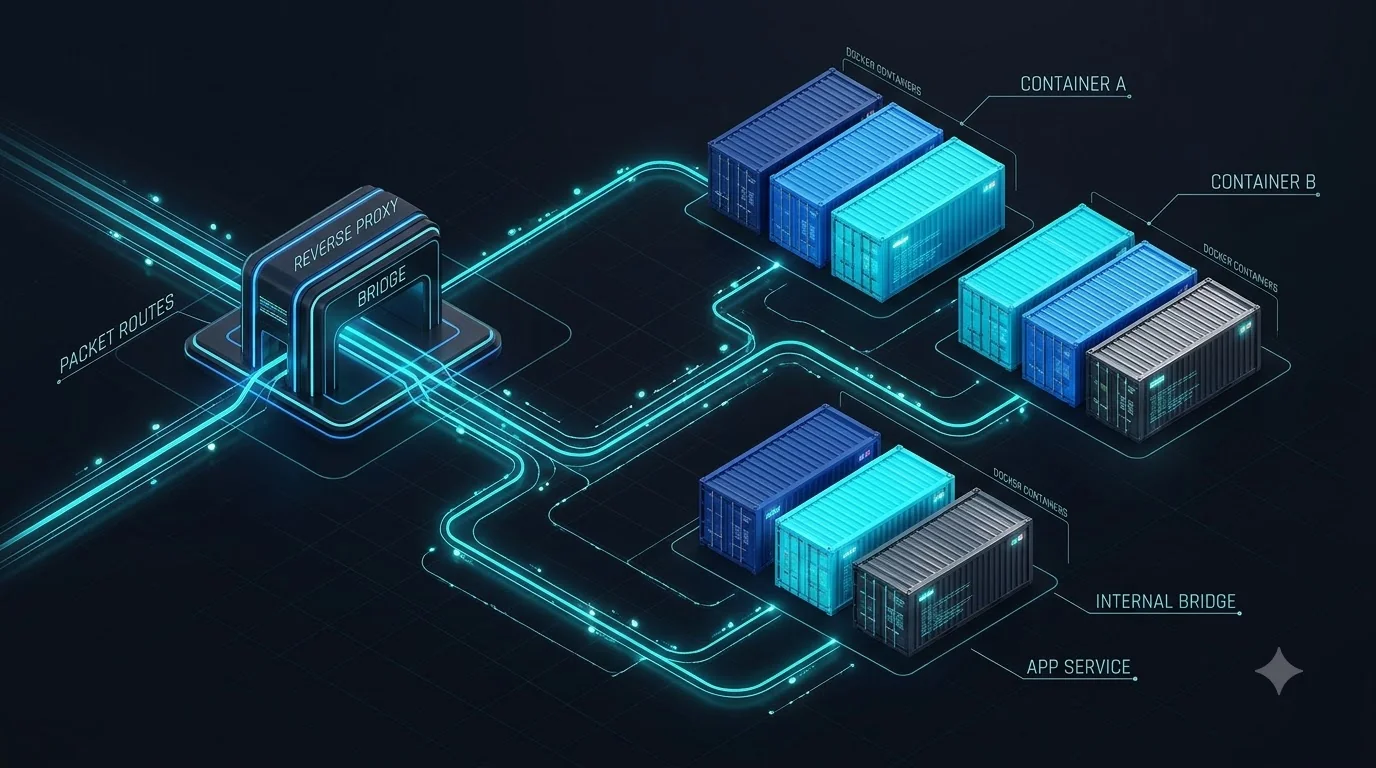
When running multi-container stacks in production, exposing host ports directly (-p 8080:80) bypasses Linux UFW firewalls via Docker’s direct iptables manipulation.
Here is how systems architects design isolated bridge networks with secure Traefik edge gateways.
1. The Docker iptables Trap
When Docker starts with default flags, it prepends rules to the PREROUTING and DOCKER chains in Linux netfilter. This means incoming packets are routed directly to containers before reaching standard host firewall rules like ufw deny 8080.
Recommended Next
Coolify
Self-Hosting Like a Cloud Provider: Complete Coolify Production Guide
How to turn a $5/mo VPS into a private Heroku/Vercel PaaS with automated Git deployments, Traefik SSL termination, and Docker clustering.
By Mohan